Get started
Test your API in 5 minutes.
Start with your own API, or use one of ours. Quick, easy, and free.
Follow along with this quick 3-minute video to see how it works.
Self-directed tutorial
Test your API in ten steps.
Step 1
Set up your free account
Fill out the simple Free Edition form to get instant access.
Step 2
Register your application
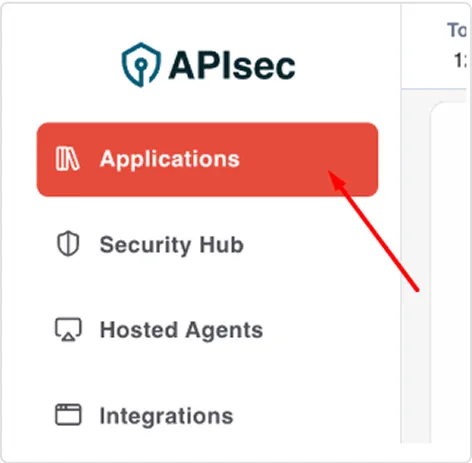
Open the Applications menu and select “Add Application.”
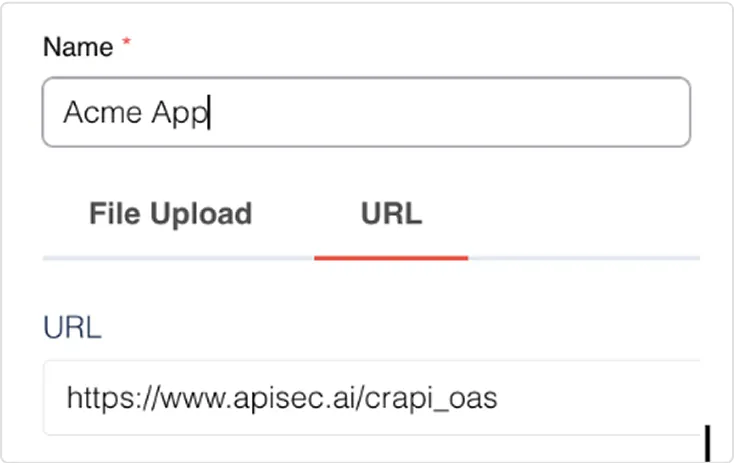
Provide an OpenAPI specification or GraphQL schema, or connect apisec to your gateway.
No API to test? Use our demo API. Select OpenAPI Spec and use the crAPI demo (see /crapi for the spec), with base URL https://crapi.apisec.ai.
Step 3
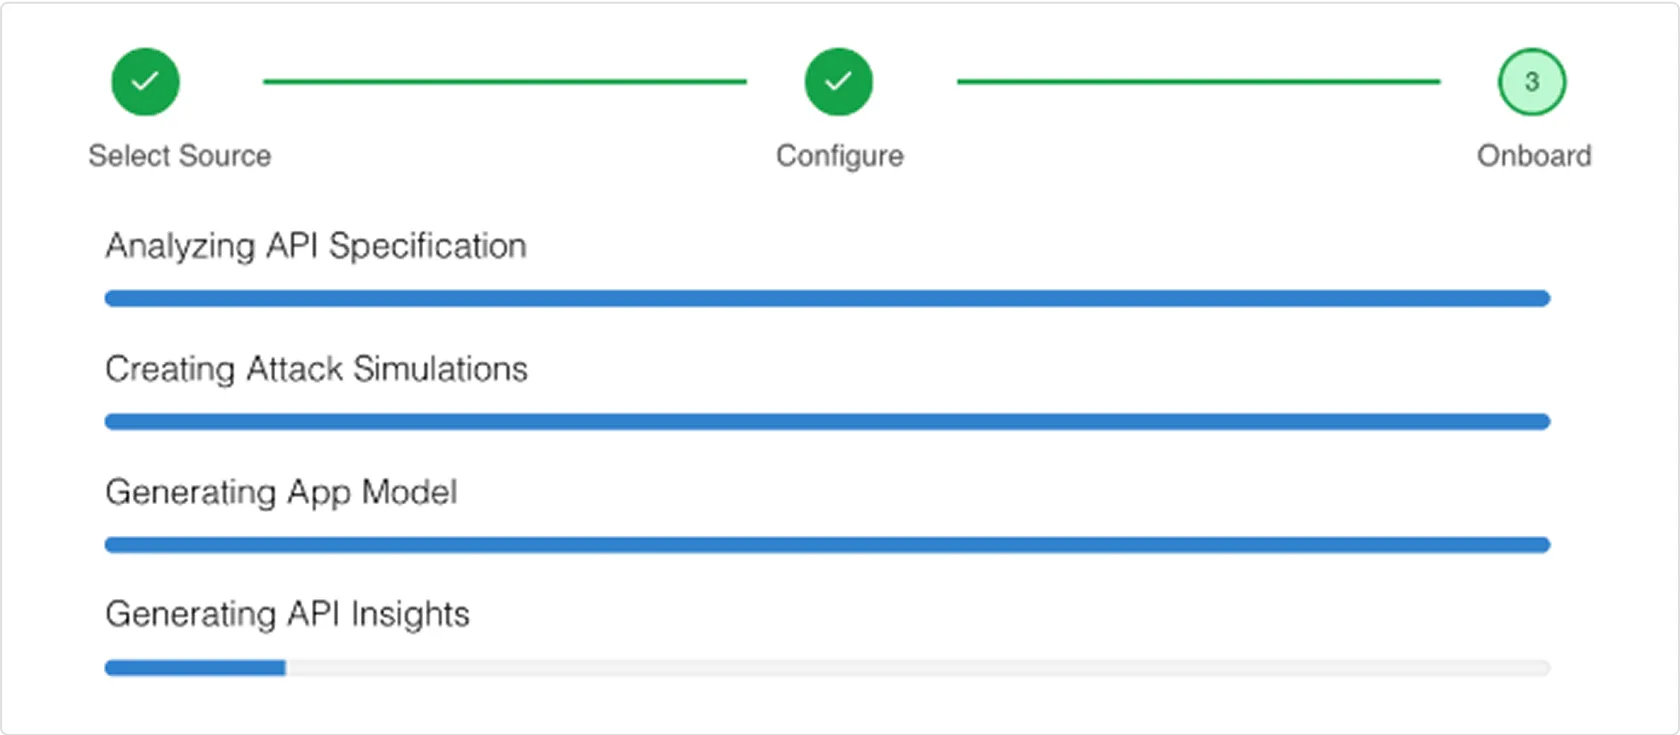
Click Onboard
apisec immediately starts analyzing your application: it creates attack simulations, generates the App Model, and produces API insights.
Step 4
Review the App Model
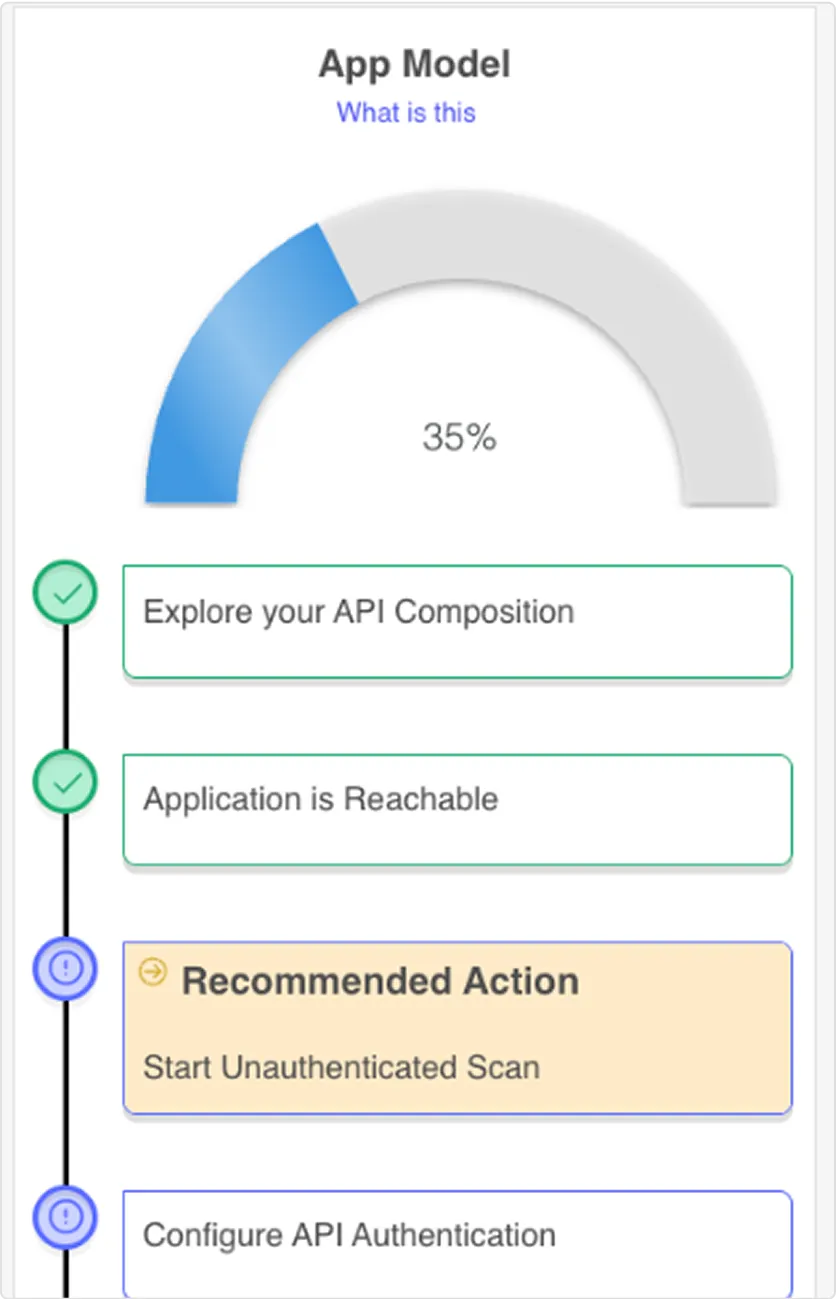
On the right you’ll find the App Model, your personal guide to getting the most out of apisec and ensuring your API is fully tested. You’ve already completed the first item, Explore your API Composition. The next is a reachability check to your target API. If your application isn’t reachable, whitelist the agent IPs or deploy a Hosted Agent.
Step 5
Explore your API
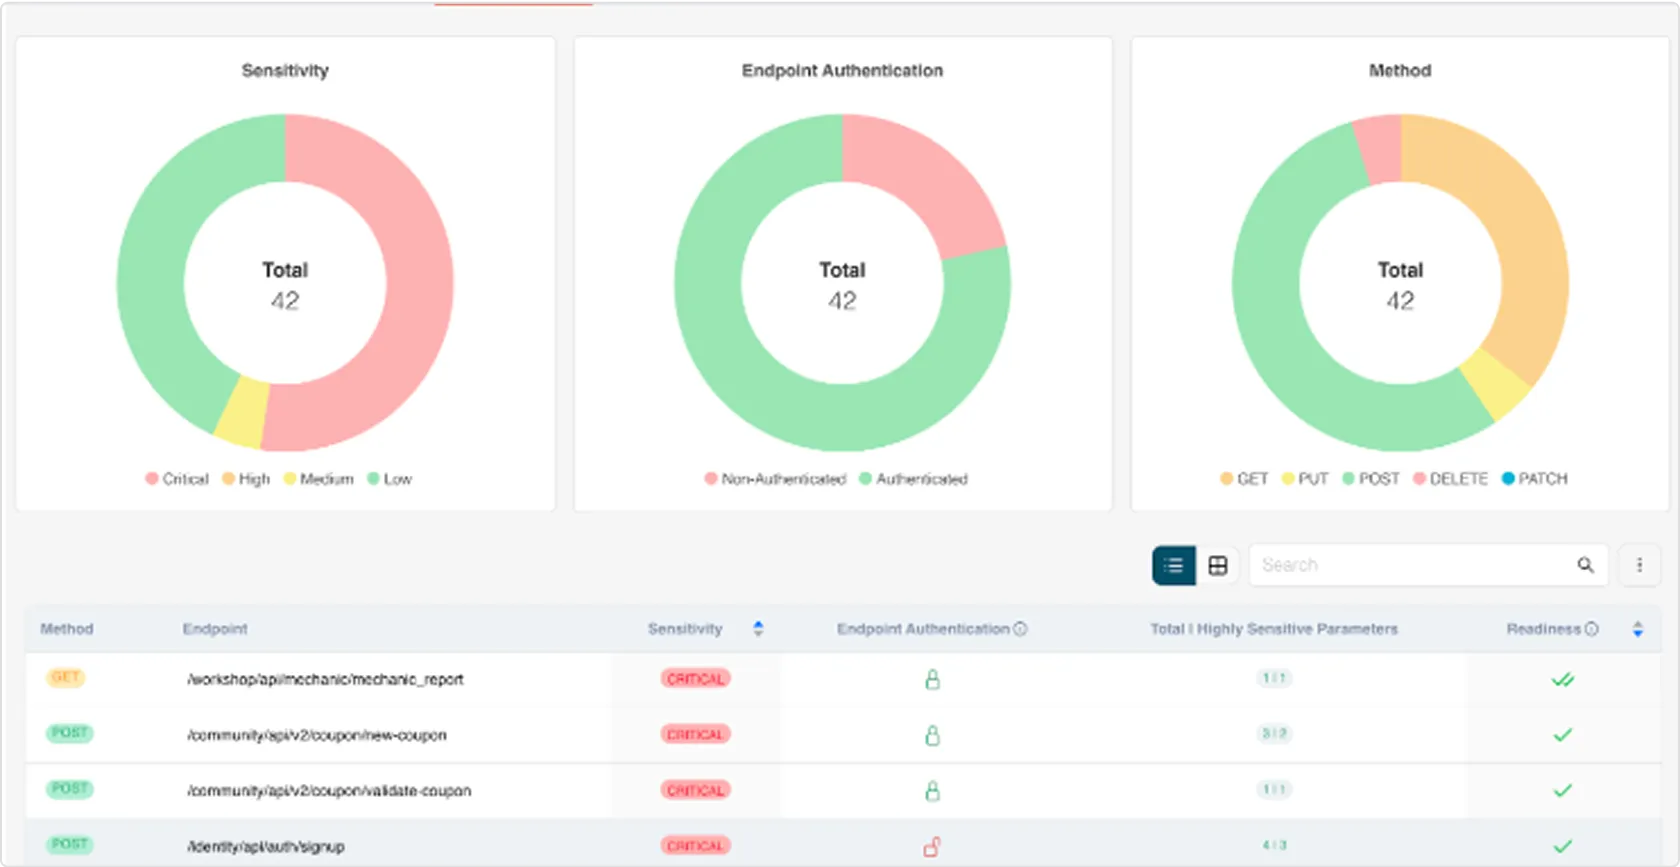
The Endpoints tab shows your API’s endpoints, the methods used, authentication status, and endpoint sensitivity. It’s fully interactive, click the chart elements to see the matching endpoints below, and click an individual endpoint to learn more about its functionality.
Step 6
Review test coverage
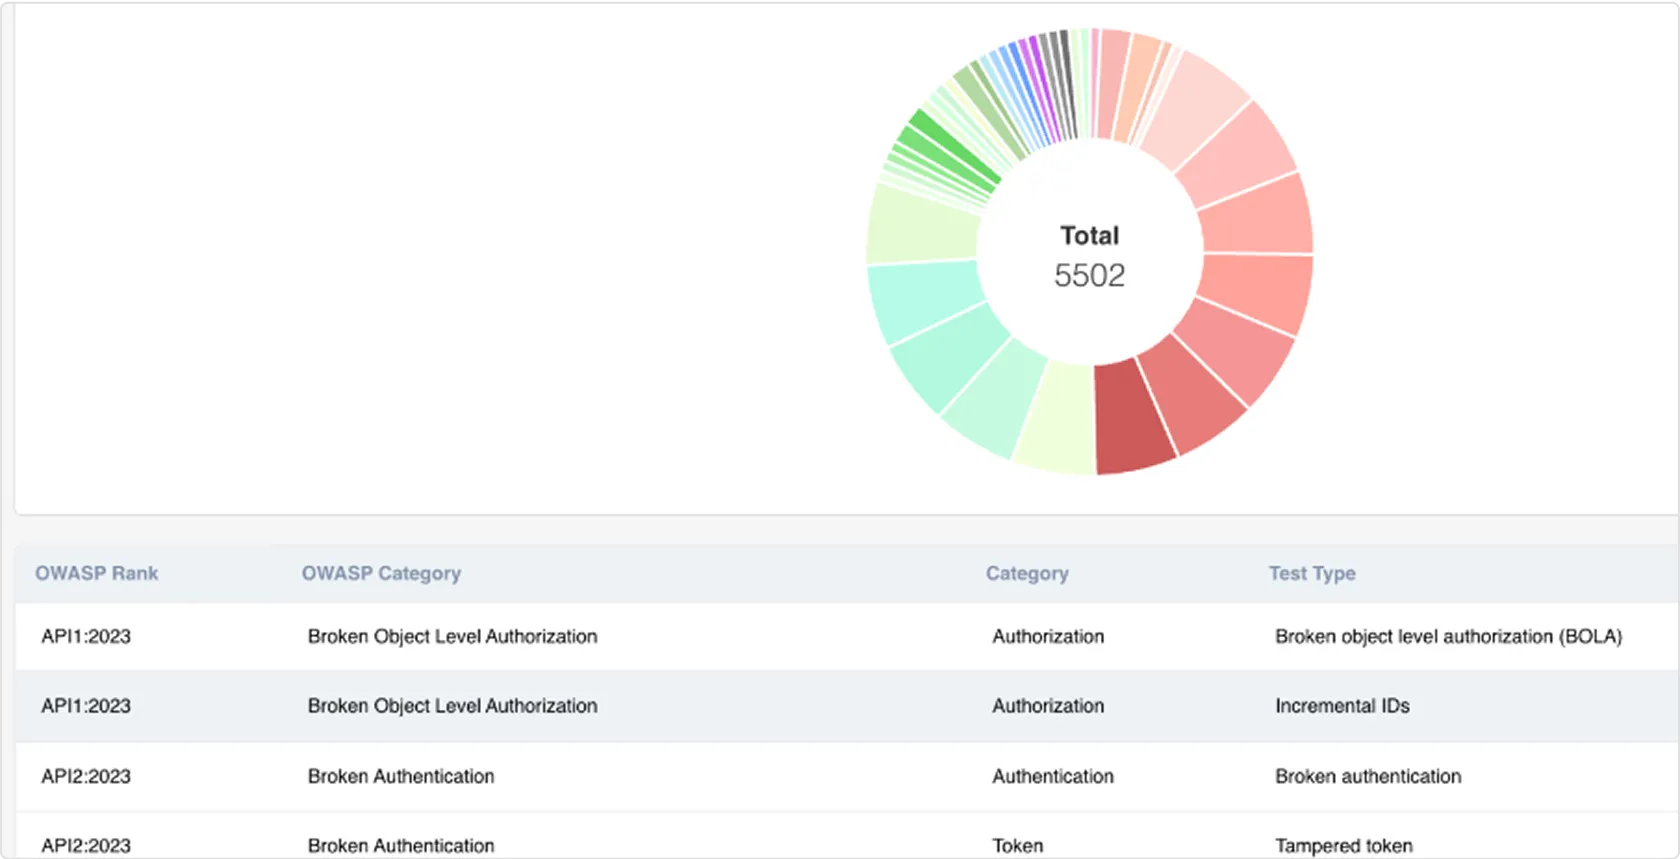
Visit the Coverage tab to see the volume and types of attack simulations generated.
Step 7
Run an unauthenticated test
Run your first active test. Check the reachability status, and deploy a Hosted Agent if your API isn’t directly reachable.
Step 8
Review findings
Review the list of detected issues and understand their impact.
Step 9
Set up authentication
Add credentials so apisec can test protected API endpoints.
Step 10
Run an authenticated test
Launch a deeper run to uncover the issues that only appear behind authentication.
Ready to secure what matters most
Start with a team that proves what’s exploitable.
Need more help